The XFA Desktop Application now runs on NixOS. Install it with the same command as on every other Linux: it goes into your own nix profile, without root permissions, and XFA keeps itself up to date. Admins who manage NixOS centrally can add XFA to the system configuration instead. See how to install XFA on NixOS
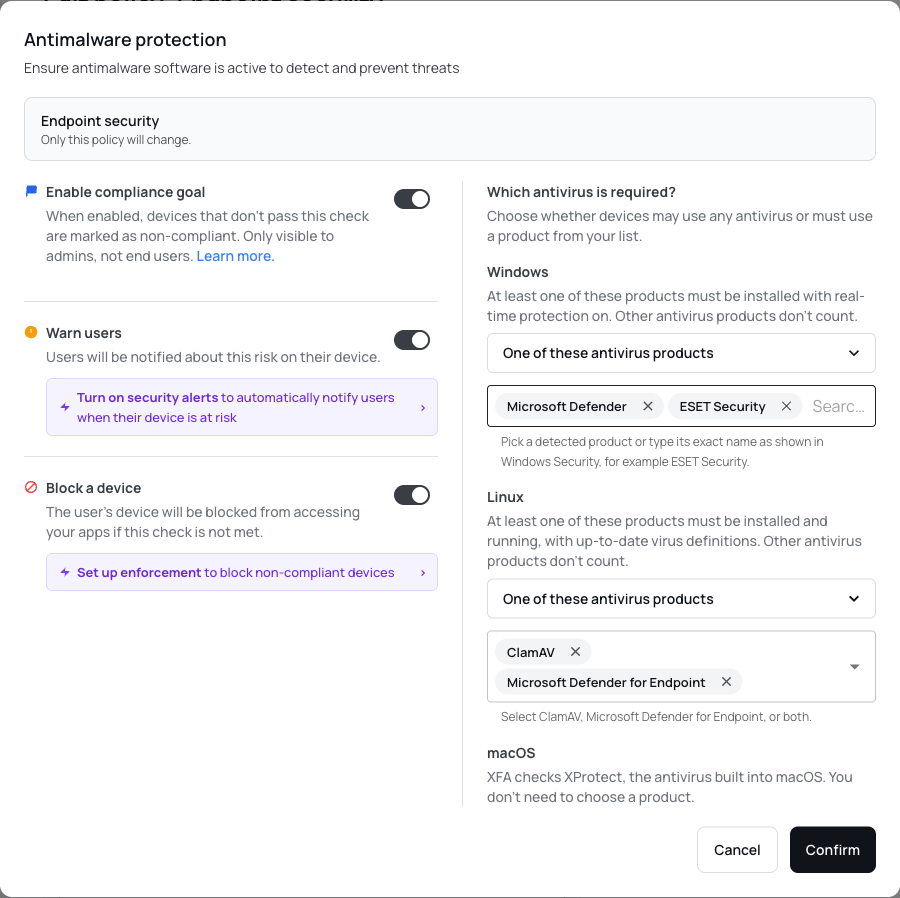
A device can have antivirus running and still be missing the product your organization requires. With this Beta enabled for your organization, you can now choose which antivirus products satisfy the policy on Windows and Linux.
On Windows, select Microsoft Defender or a product registered with Windows Security Center, with suggestions from your device inventory. On Linux, choose ClamAV or Microsoft Defender for Endpoint. Device details, the sign-in verification screen and risk emails explain the required and detected products, so users can see why a check needs attention. Configure your device policy
An OS version policy no longer has to make the same choice for every platform. Set separate requirements for Windows, macOS, Linux, Android, iOS and iPadOS, for example when your Windows rollout and your mobile update schedule need different warning or blocking windows.
Keep the platforms synchronized to one shared version policy, or give individual platforms their own settings. iPadOS has its own version policy too. Review your device policies
The desktop app now has a personal view for checking your computer's security, even when you are not connected to an organization. A new setup wizard helps you get started, and separate views for each organization show which checks that organization requires.
You can also add personal checks alongside your organization's checks and choose which personal findings to ignore. Your personal choices stay separate from the requirements your organization sets, so it is clear what needs your attention and why.
Documentation: read the guides in English, Dutch, German, French, Spanish, Finnish or Portuguese, with search available in all seven languages.
Open the XFA desktop or mobile app, enter your work email and confirm it with a one-time code. XFA then shows the organizations you can connect to, so you can get started without asking an administrator to send a separate invitation.
Administrators decide whether their organization allows this through self invite in Awareness settings, where the feature is marked Beta. Connect from the XFA app
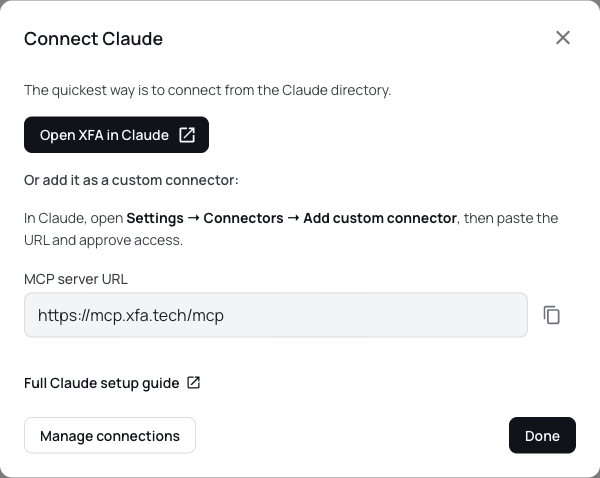
Connect Claude, ChatGPT or another compatible AI assistant to XFA and ask questions in your own words: which devices are out of date, who still has no verified device, or how your security posture has changed over the last three months. The assistant reads your organization's device, compliance, policy and software-version data through the Model Context Protocol (MCP), so you can explore it in a conversation.
You choose which organization to connect and approve read-only access. Connected apps in the dashboard shows those connections and lets you revoke access whenever you need to. Connect your AI assistant
Organizations that already use Microsoft Intune, Configuration Manager or Jamf can now pre-install XFA and connect devices with their organization's enrollment token. Instead of waiting for each person to install the app, add XFA to your existing deployment so its checks are in place when people start using their devices.
The dashboard provides the setup steps, packages and commands for the rollout. MDM pre-installation is available on Enterprise. Deploy XFA through your MDM
The redesigned dashboard overview brings the status of Discovery, Awareness and Enforcement together with device posture, known risks and recent activity. See where your rollout stands, which risks need attention and what to do next, without piecing the picture together from several pages.
Recommendations point to the next useful setup or security action. The posture and risk cards keep the numbers alongside their explanation, so you can move from an overview to the devices that need a closer look. Open your dashboard
XFA now lets you set a default language for your organization under Settings → Organization. When someone's own language is not known, XFA uses this default for their emails and messages instead of falling back to English. A user's own language, detected automatically or set on their profile, is always used when it is known.
MFA requests now reach you through a system notification on Windows, macOS and Linux. Approve or deny the request from the notification itself, instead of having to open the XFA tray menu to find it.
Dashboard: rolling-release Linux devices show the basis for their OS assessment, including the last full update and local package vulnerability information, instead of treating “rolling” as a version number.
Windows on Arm devices now have a native XFA build, rather than running the x64 app through emulation. Existing installations move across through the normal updater: first they receive the update that recognizes Arm devices, then a later update brings them the native build.
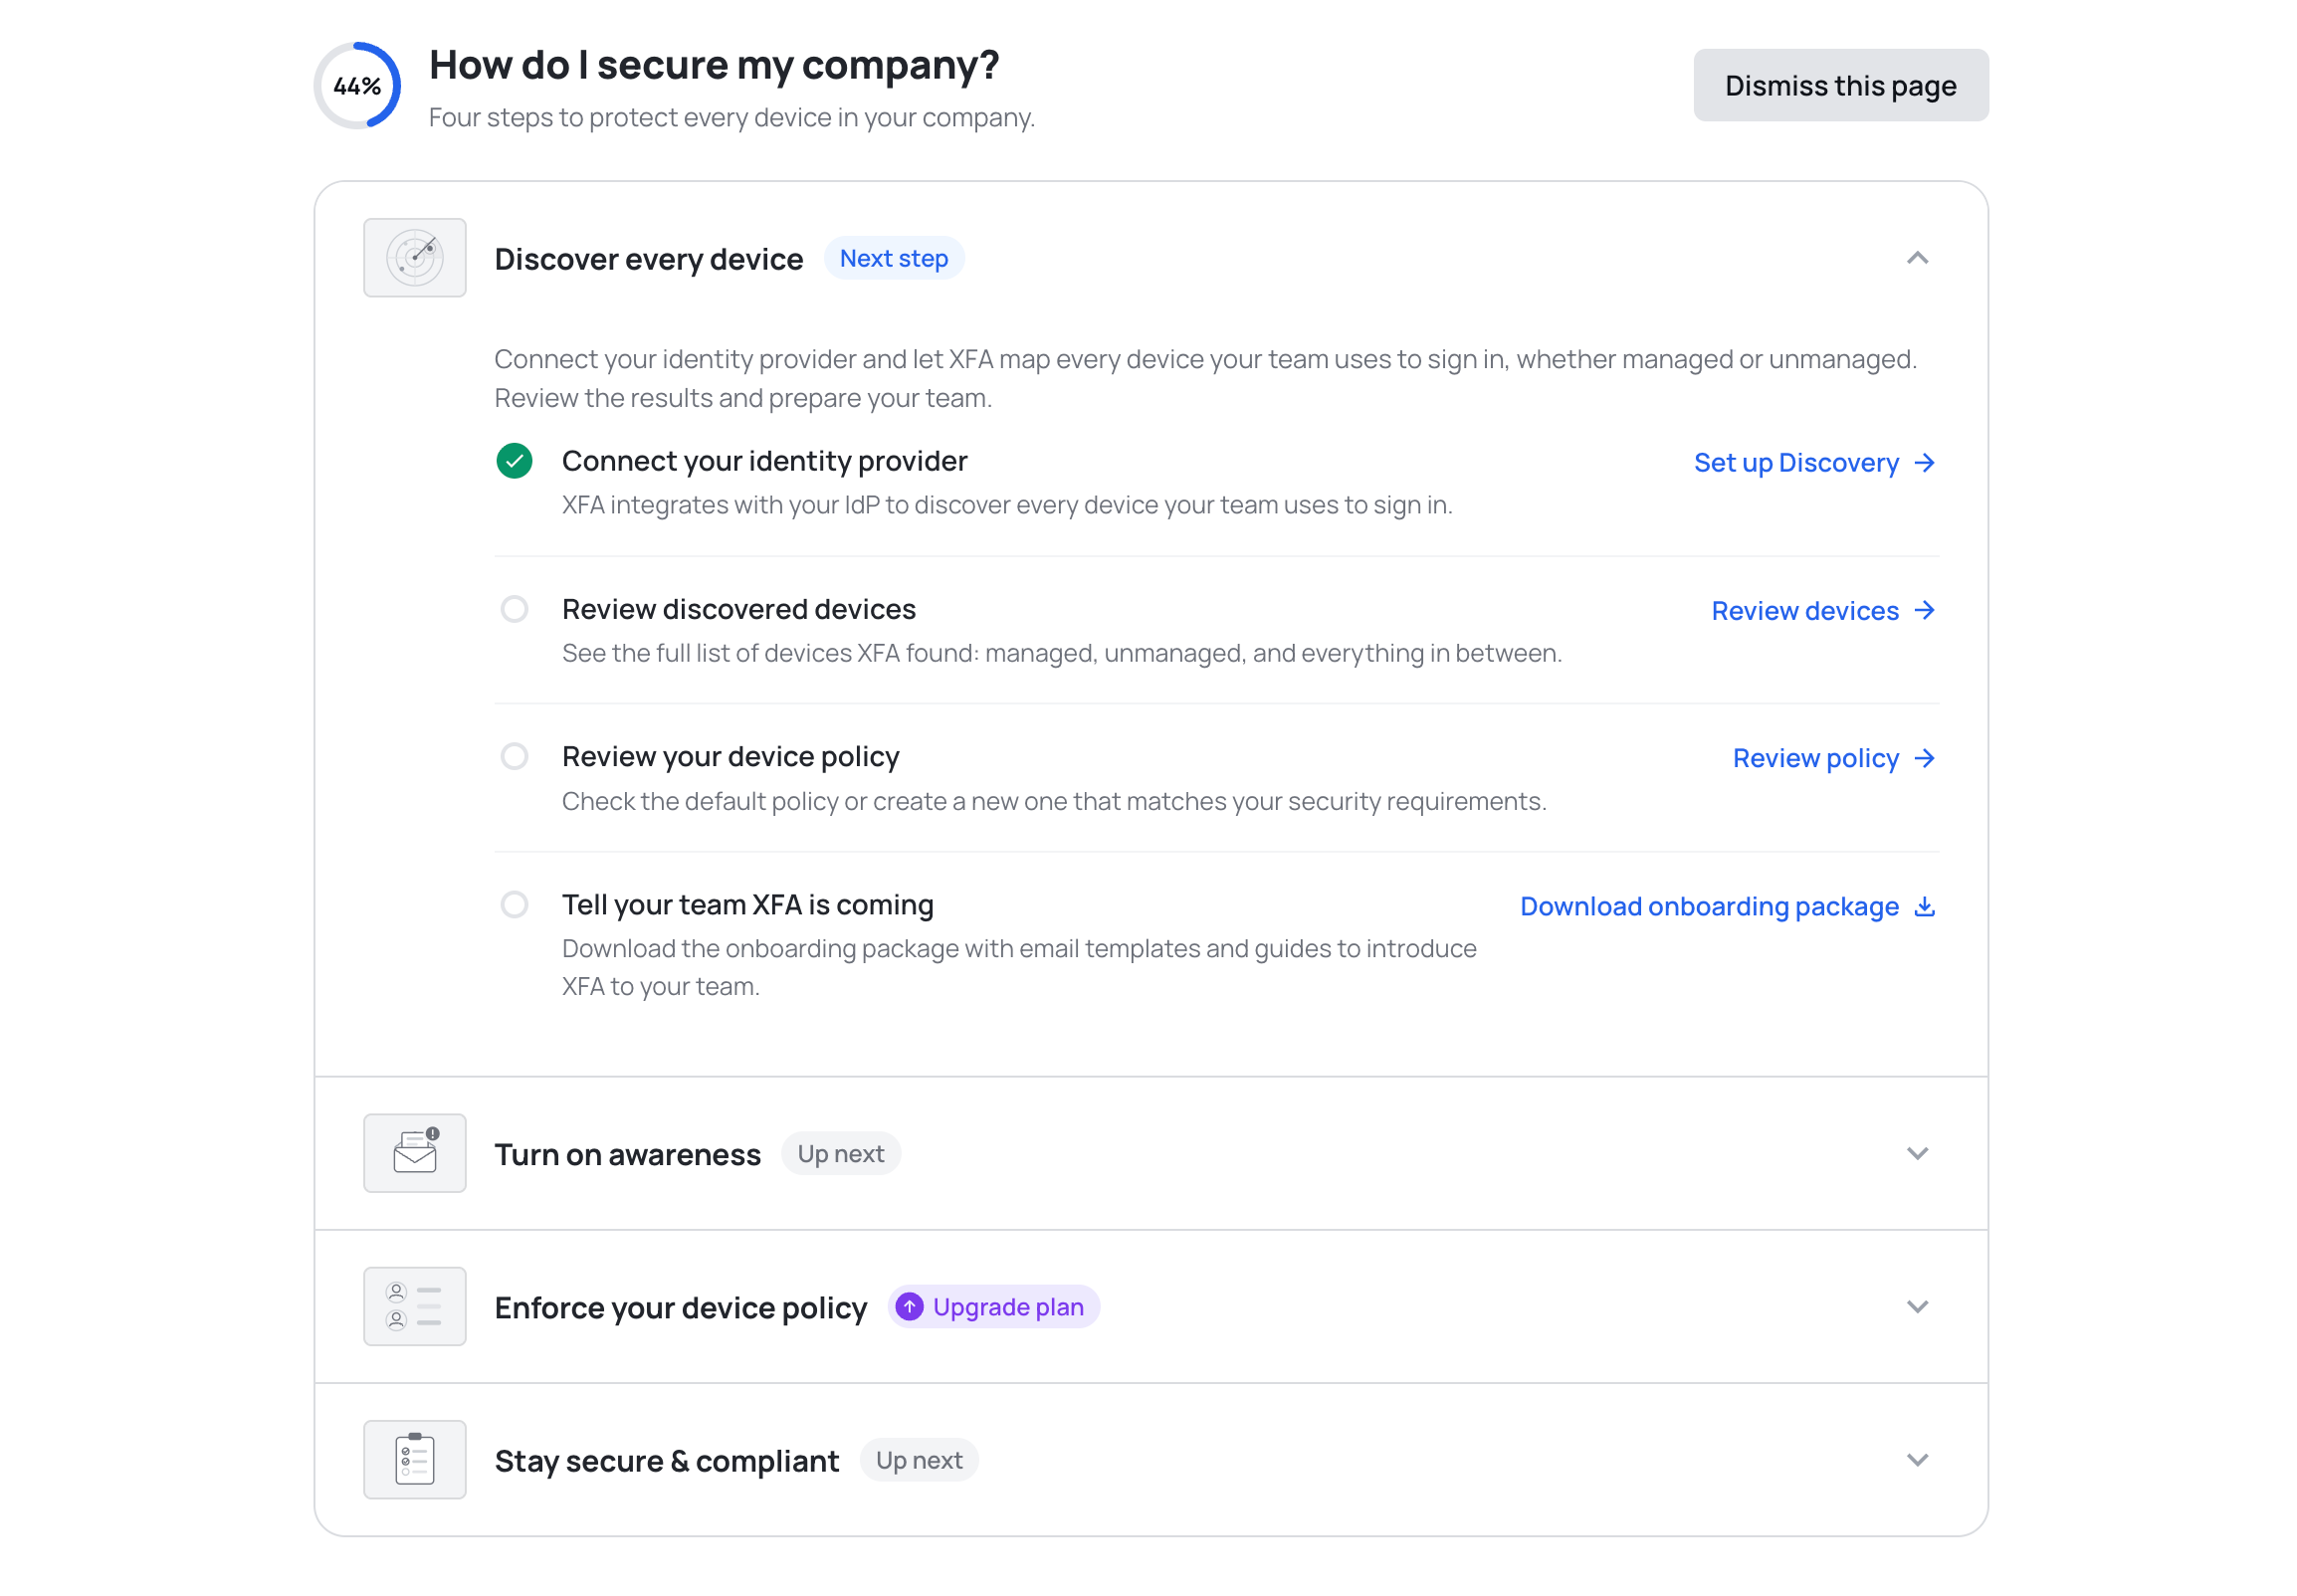
The new Getting Started page helps you get more out of XFA. It lays out four tracked steps, from discovering every device to staying secure and compliant, so you always know what to set up next.
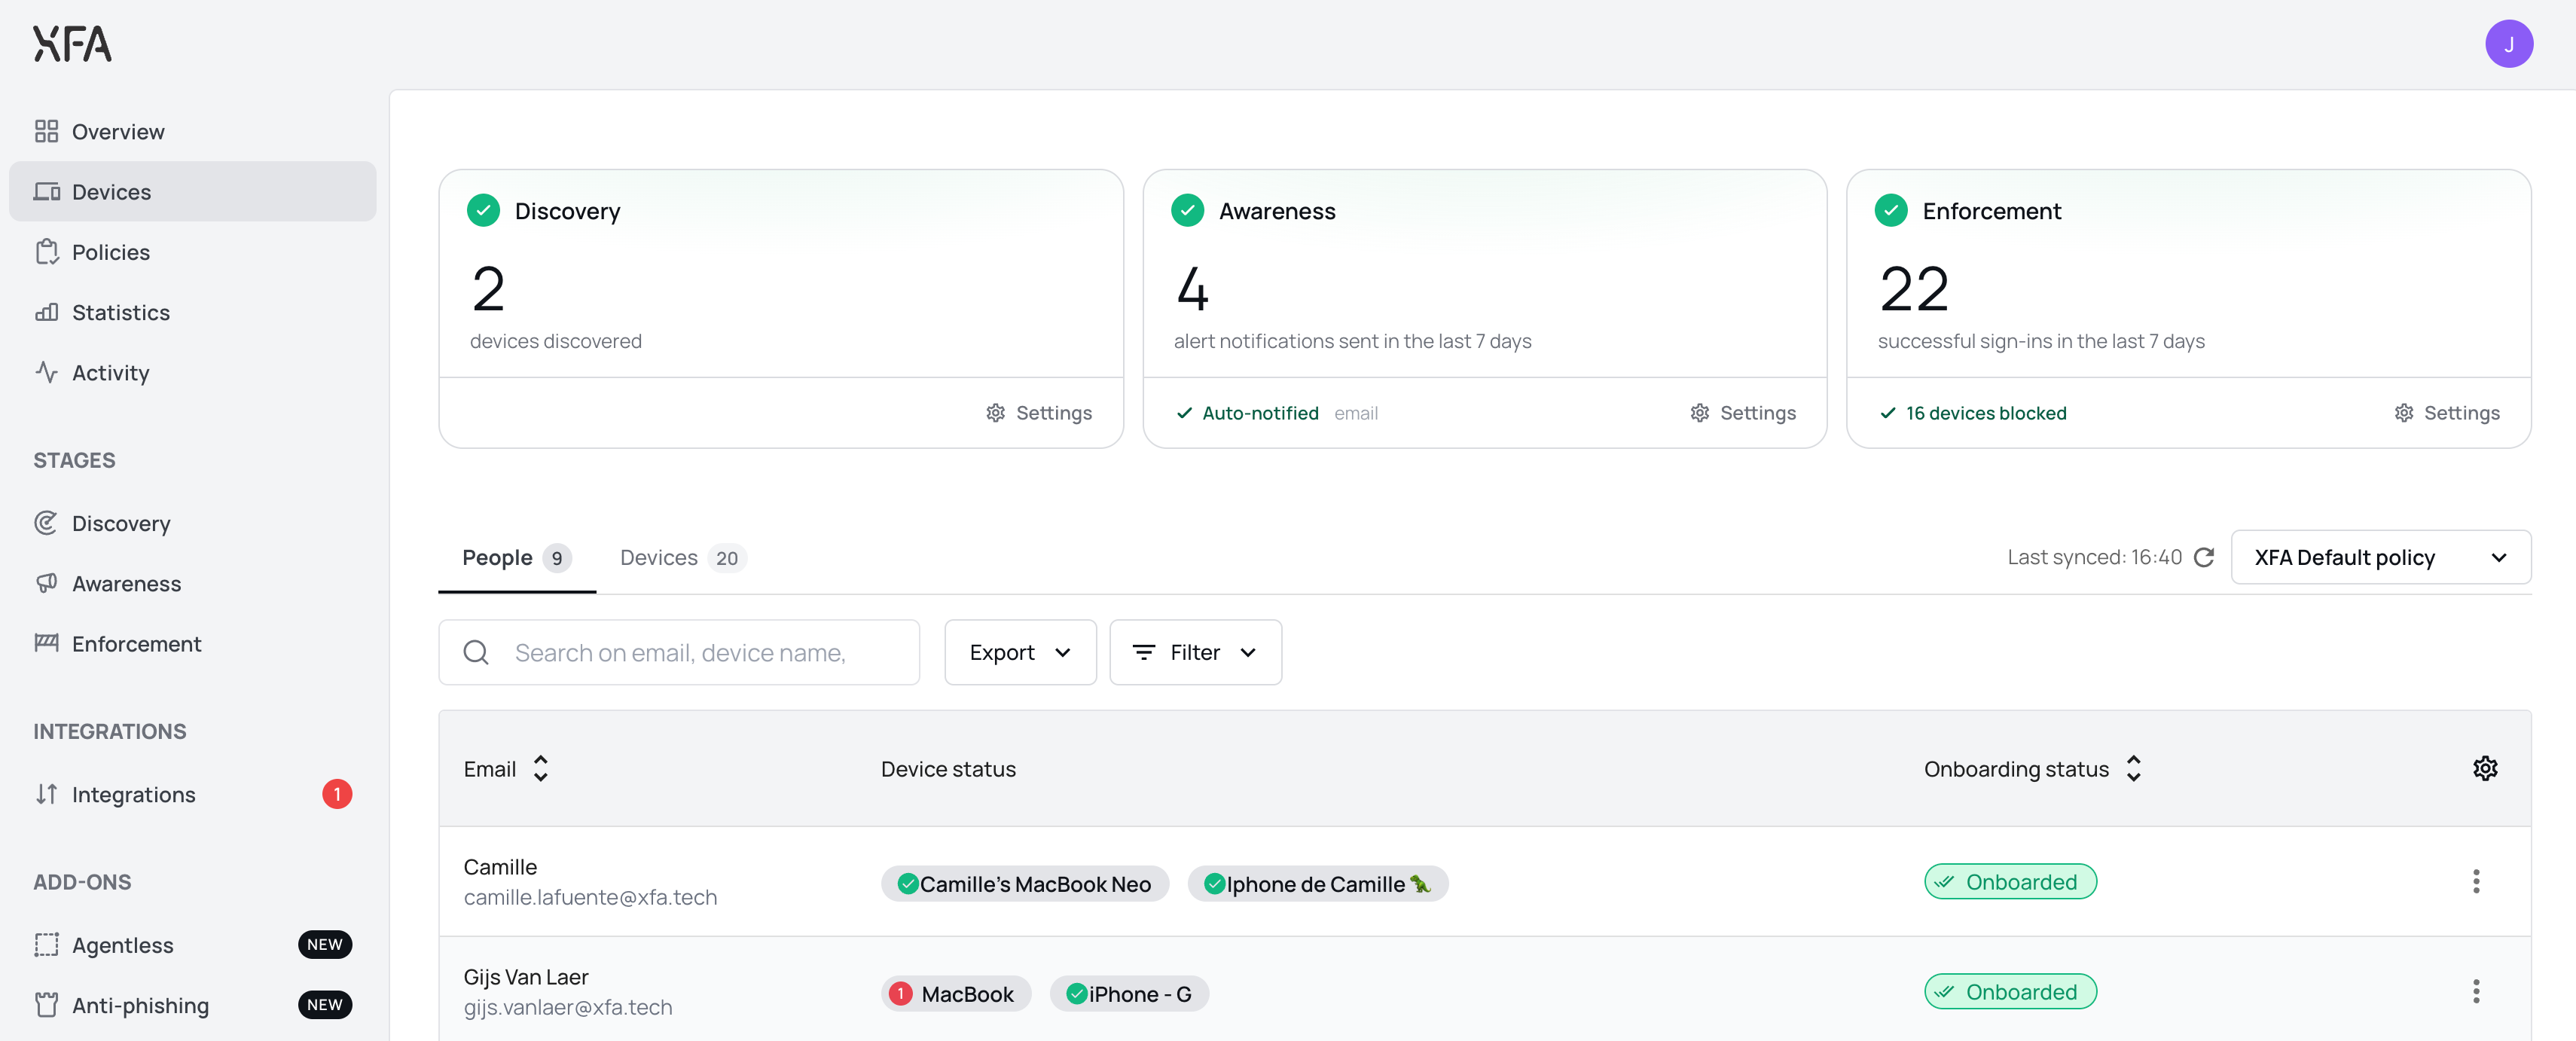
The Devices page now opens with a card for Discovery, Awareness and Enforcement, so you can see at a glance where your organization stands. Each card says whether that pillar is running or waiting on you, with the number behind it: devices discovered, alerts sent, successful sign ins. See the Devices overview
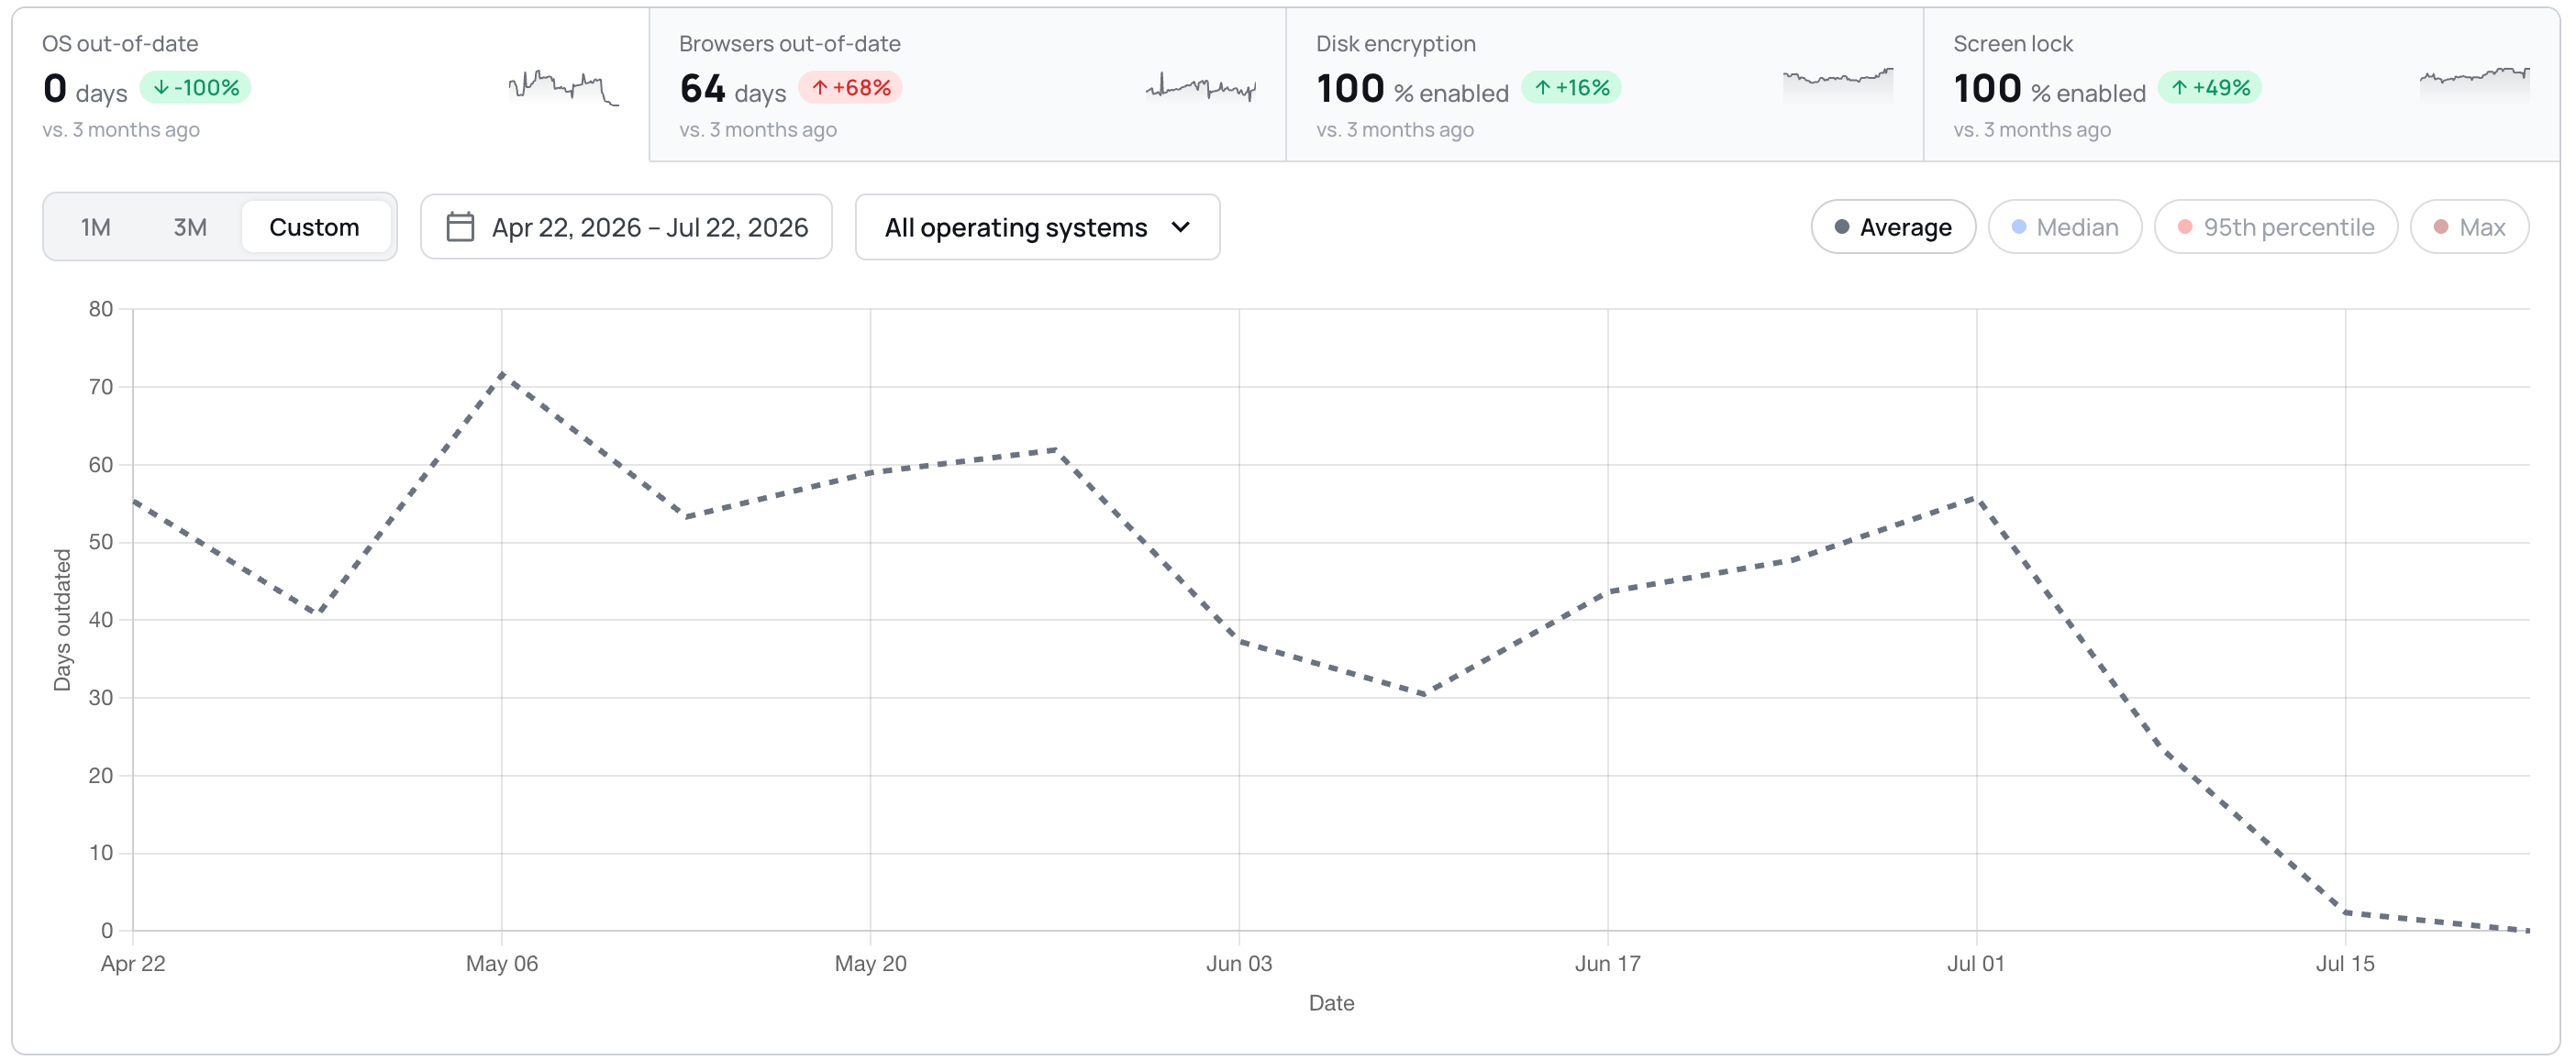
Trends are now a single card: four tiles act as tabs above one chart, with the period, the operating system filter and the chart type on the card instead of in a fullscreen modal. Custom date ranges are supported, and the BETA labels are gone.
The device detail view now reports whether a device allows unattended remote access, and explains what the check looks for. You can act on it in your policy; XFA does not change the setting on the device. See your device policy
Dashboard: a Discovery integration that was never connected now shows a red alert and a Reconnect button, and counts towards the Discovery badge.
Dashboard: smaller interface fixes throughout, including larger tooltip and dismiss targets, steadier invoice rows, and long organization names that truncate instead of pushing controls off screen.
Dashboard: the Discovery page no longer shows a next run in the past. It is now anchored to the coming hour.
Dashboard: confirming a delete no longer leaves the button spinning. The dialog closes once the delete succeeds, and shows an error if it fails.
Desktop: the screen lock timeout row now shows a warning icon when the check fails on the timeout, instead of staying green while the check warns.
Desktop: the OS updates check now follows your policy grace in the app, the systray and the web flow alike.
Desktop: eighteen strings in the check details and fix actions are now translated in German, Spanish, French and Dutch, instead of falling back to English.
Mobile: approving MFA on another device no longer leaves the mobile app waiting.
The checks that flag a jailbroken, rooted or developer-mode device, or one that was just rebooted, already ran in the XFA app and showed in your dashboard. They now also reach the access decision at sign-in for mobile devices, so a risky mobile device is warned or blocked at login per your policy, the same way it already is on desktop. Nothing new is installed: the mobile app simply reports these signals when it verifies the device at sign-in. See your device policy
Dashboard: a lighter, more responsive feel, with smoother transitions, clearer hover and loading states, skeleton placeholders while data loads, and success confirmations that appear only once an action has actually saved. Motion respects your reduced-motion setting.
Dashboard: notifications are rebuilt to be calmer and more legible, and no longer duplicate, flicker or jump when several arrive at once.
Dashboard: Discovery and Enforcement now have a Watch demo action that opens a short guided tour without leaving the dashboard.
Desktop: the device-lock check now applies your organization's maximum screen-lock timeout, so it no longer shows OK in the app while sign-in is actually being blocked.
Desktop: the OS updates check on Fedora Linux is much faster, and no longer reports a device as out of date right after a reboot before its update data is ready.
Dashboard: setting up Google Workspace discovery no longer skips the domain-wide delegation step. You now confirm delegation is configured before continuing.
Web app: MFA and TOTP sign-in are more reliable. Trusted devices register after approval, malformed device tokens are refreshed instead of failing, and TOTP email confirmation links open the right step.
Dashboard: fixed a rare case where the dashboard could get stuck reloading right after a new version was deployed.
Dashboard: fixed a redirect loop that could bounce you back and forth during MFA sign-in.
Dashboard: blocked-account access handling is more consistent, and you now review your billing details before checkout.
Dashboard: an invited user's signup now always uses the invited email address, even if an earlier unfinished signup was left in the browser.
Setting up an Enforcement policy no longer means guessing what will happen. The policy settings now show a threshold timeline and a live timing summary as you edit, plus suggestion chips for common warn and block windows. You can see precisely when a device would be warned, and when it would be blocked, before you save. Enforcement stays configurable: a policy can warn or block, with or without an Awareness notification. Set up a policy
Discovery has a redesigned two-column overview and a clearer way to add a connection. Selecting Add connection now opens a provider picker for Microsoft, Google or Okta and takes you straight to a step-by-step setup page for the one you chose. Discovery reads the devices in your organization from a connected identity provider, so adding one is the first step to seeing every device in use. Connect Discovery
Dashboard: the Devices table now shows whether a device's Last Seen came from the XFA agent or from Discovery.
Dashboard: billing details and the change-address flow moved into a redesigned Subscription section, and adding a payment method now asks you to pick a plan first when none is active.
Dashboard: an account blocked for billing can still open Settings to download its invoices.
Dashboard: the Overview shows its shell and skeletons immediately for a faster first load, removing the blank white first paint.
Dashboard: the onboarding language switcher now uses the shared dropdown for a consistent look.
Integrations: you can now disconnect a Microsoft Teams connection from the Integrations page, the same as Slack.
Web app: the install and MFA screens have a refreshed layout and clearer copy.
Dashboard: the app now reloads itself once after a deploy instead of erroring on a stale page chunk.
Dashboard: the device-notify popup hides right away after you choose Don't show again.
Integrations: reconnecting Vanta no longer fails with a 500 error.
XFA now talks to your team in Microsoft Teams. Connect your tenant once, and end users receive device risk alerts, new-device enrollment invitations, and sign-in verification requests as direct messages — no email required.
Admins stay in control: toggle each notification category on or off, send a test message per section, and connect the tenant from the Integrations page in your Dashboard. Messages are localized in English, Dutch, French, German, and Spanish.