Enable Agentless sign-in in a policy
Agentless sign-in is turned on per policy, and applies to every application that uses that policy. Before you turn it on, choose the data sources XFA can use on the Agentless page of the dashboard. See Agentless verification for an overview.
Your XFA plan must include Agentless verification. If it does not, the dashboard locks the setting and shows an upgrade prompt.
If your policy relies on signals from managed Chrome profiles, finish the Chrome Device Trust setup first.
Enable Agentless sign-in
- Go to Policies in the XFA Dashboard.
- Open the policy you want to change.
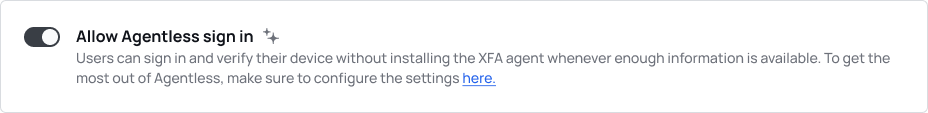
- Turn on Allow Agentless sign in.
- Save the policy.
Verify it worked
Open an application that uses the policy in a supported browser. Agentless sign in appears when XFA has enough information to evaluate the device against the policy.
If the option is not available, check that the Agentless data sources you need are turned on and can provide every signal the policy asks for. For managed Chrome profiles, see the troubleshooting steps in Configure Chrome Device Trust.
Agentless sign-in and MFA
Agentless sign-in can be used with MFA. However, Device approval after MFA, when enabled for your organization, requires the XFA app on the sign-in device and makes Agentless sign-in unavailable, even if you use TOTP on another device.